· Business
NZ Privacy Act amendment, IPP 3A is now in force. Indirect data collection requires notification.
Here’s what we’ve seen across the market:
- Some firms updated their privacy authorisation wording
- Some have real systems programmes planned, but not live
- Most did nothing and are quietly non-compliant
Some firms didn’t realise they were affected at all, particularly those collecting data via API from third parties.
There’s a difference between:
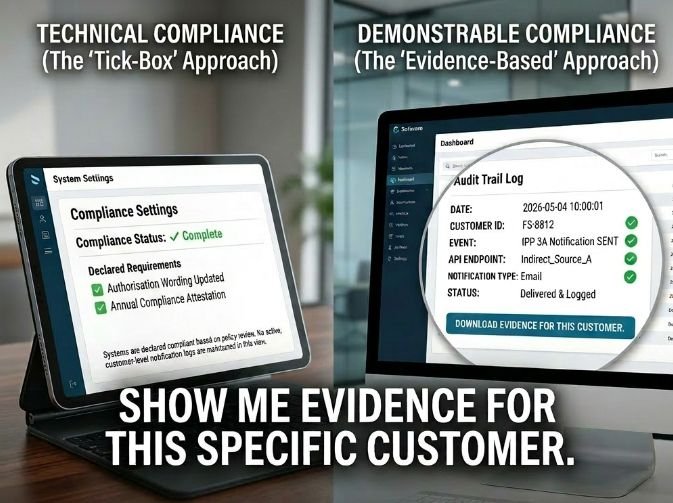
- Technically compliant
- Demonstrably compliant
Most firms chose the first. A clause was added. A box gets ticked.
But the underlying system didn’t change.
- No notification workflow
- No audit trail
- No evidence of what happened, when, and for whom
The problem only shows up when the question changes:
“Show me how this requirement is implemented” becomes “Show me evidence for this specific customer”.
Can you produce evidence of a notification for a specific individual, on a specific date?
If not, you have coverage on paper, not compliance in practice.