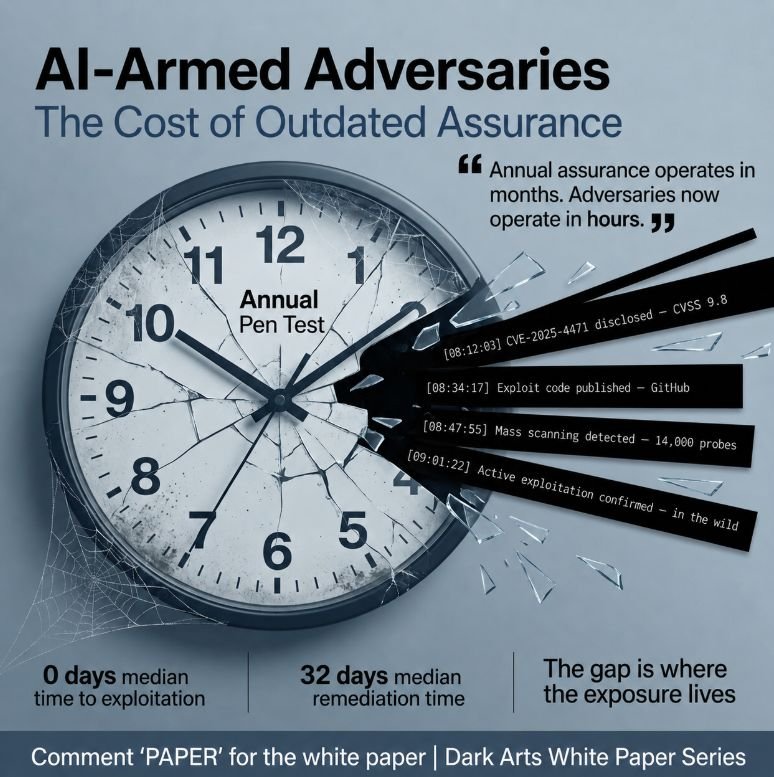
An annual pen test is necessary. For many firms, it is also mandatory. But on its own, in 2026, it is no longer sufficient.
A pen test gives you a two-to-four-week window of expert human testing against a scope defined before the test began. But it is a snapshot. The findings reflect your code, your dependencies, and the threat landscape on that one day.
Every day after, the picture decays. Code changes. Dependencies update. New vulnerabilities are disclosed. By the time next year’s test begins, the report describes a system that no longer exists.
Here is the problem in one line: annual assurance operates in months. Adversaries now operate in hours.
Verizon’s 2025 DBIR found that for known-exploited vulnerabilities, the median time from disclosure to mass exploitation is zero days. A once-a-year test cannot see a window that opens and closes between tests.
An annual report that is months out of date by the time it is filed may still satisfy the auditor. It no longer gives the business operational assurance. The gap between those two things is where the exposure lives.
This is not an argument against pen testing. It is an argument for what wraps around it.
Continuous AI-assisted scanning is now commercially available. So is AI-assisted remediation, from suggested secure fixes to testable patches. None of it replaces the annual test. It closes the gap between one snapshot and the next.
The firms that close that gap will not do so by asking the same teams to patch faster inside the same model. They will do it by changing the unit of measurement: from annual assurance to continuous detection, remediation, and proof.
Defending at human speed against machine-speed adversaries is not a control. It is a hope.
We published the full analysis, including what continuous assurance actually looks like, in our latest white paper. Get in touch and I’ll send you a copy.