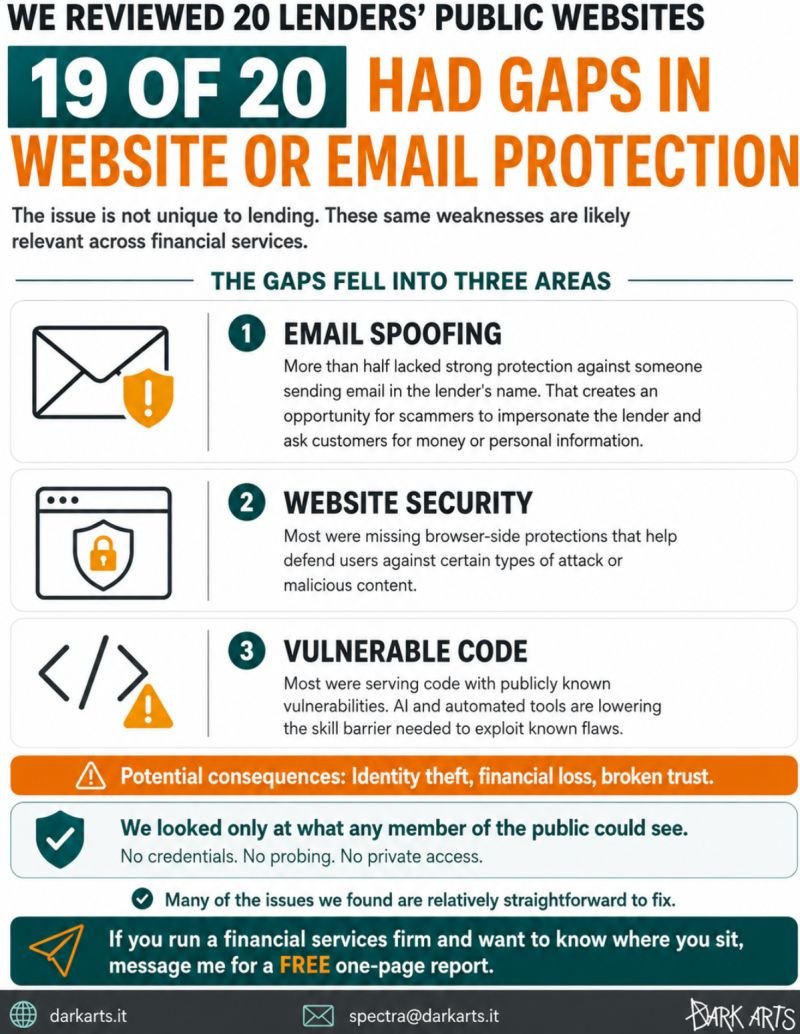
Last week I shared the headline numbers from our review of twenty lenders’ public websites. This is the first finding in detail, because it is the one that worries me most.
The gaps fell into three areas:
Email Spoofing: More than half lacked strong protection against someone sending email in the lender’s name. That creates an opportunity for a scammer to impersonate the lender and ask a customer for money or personal information.
Website Security: Most are lacking protections a browser relies on to keep a visit safe. That makes it easier for a bad actor to intercept or tamper with customer communications.
Vulnerable Code: Most companies are serving code with publicly known flaws. Exploiting a known flaw used to take advanced technical skills, but now an unrestricted AI model can explain exactly how to weaponise it.
The consequences? Identity theft, financial loss and broken trust.
We reviewed lenders, but none of these findings are unique to lending. They are relevant across financial services.
We looked only at what any member of the public could see.
Many of the issues we found are relatively straightforward to fix.
If you run a financial services firm and would like to see how your site performs, get in touch and I will send you a free one-page report.